Security at AlmaLinux
AlmaLinux OS je navrhnutý tak, aby bol transparentný, overiteľný a nezávisle certifikovaný. Od podpísaných balíčkov a verejných errata až po nástroje na kontrolu súladu s požiadavkami a formálne certifikácie - tu sa dozviete, ako vám pomáhame dôverovať systému, ktorý tvorí základ vašej práce.
How we approach security
Four ideas shape everything we do around security: keep it transparent, make it verifiable, give you the tools to prove compliance, and back it with independent certification.
Transparency
Verejné errata a upozornenia pre každú vydanú opravu.
Verifiable supply chain
Signed packages and a Software Bill of Materials you can check.
Compliance and hardening
OpenSCAP, OVAL, and CIS tooling to audit and harden your systems.
Independent certification
FIPS 140-3 validated and Common Criteria certified, with more underway.
What we provide
Toto sú stavebné bloky, ktoré vám AlmaLinux poskytuje na zabezpečenie, overovanie a auditovanie systémov — od bezpečnostných upozornení, ktoré zverejňujeme, až po nástroje, ktoré sami spúšťate. You can also subscribe to the Bezpečnostný mailing list AlmaLinuxu to get advisories as soon as they are published.
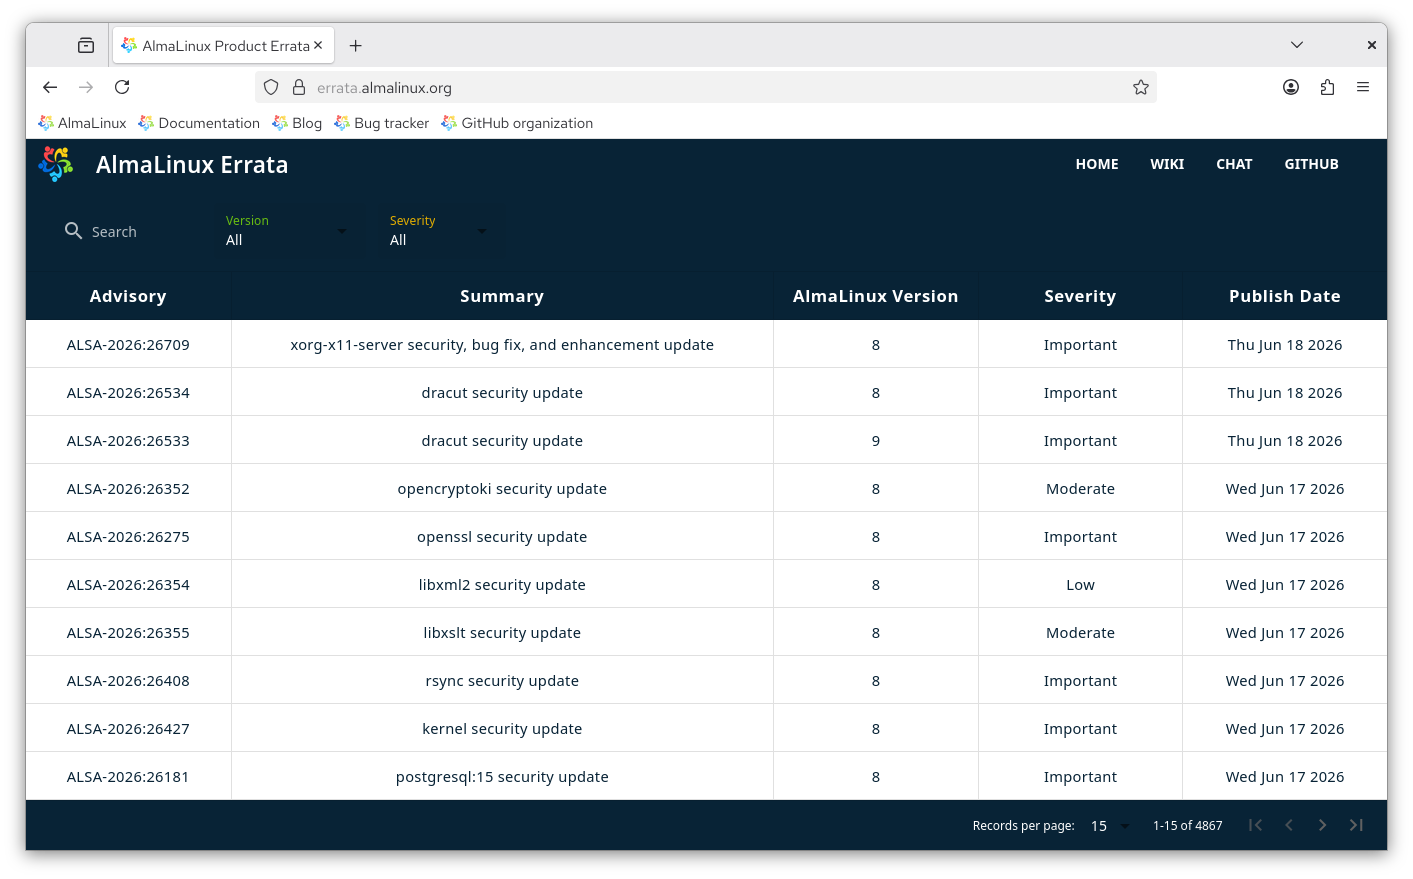
Errata a bezpečnostné upozornenia
Zverejňujeme errata pre bezpečnostné problémy a opravy chýb s analýzou ich dôležitosti.
Signed packages
Every package is signed with a GPG key and verified by default when you install it.
Compliance and hardening
Audit and harden your systems with the OpenSCAP and SCAP Workbench guides and the CIS Benchmark.
Vulnerability data
Public OVAL streams provide machine-readable vulnerability information for AlmaLinux OS 8, 9, and 10.
Software Bill of Materials
Náš systém zostavovania vytvára SBOM na zabezpečenie sledovateľnosti a bezpečnosti dodávateľského reťazca.
Secure Boot
AlmaLinux supports Secure Boot, with a shim signed by Microsoft, so systems boot only trusted software.
How we respond to security issues
The volume of disclosed vulnerabilities keeps rising, and AI-assisted research, proof-of-concept creation, and public disclosure are accelerating it further. No distribution can promise to fix every vulnerability on every timeline. What we can offer is a clear, consistent process for how we handle them.
Patching from upstream
Pri väčšine opráv sa riadime upstreamom. AlmaLinux OS sa zostavuje z rovnakých zdrojových kódov ako ostatné systémy v ekosystéme podnikových distribúcií Linuxu, takže keď upstream vydá opravy, zostavíme ich, otestujeme a zverejníme. Každá bezpečnostná oprava je vydaná vo forme bezpečnostného upozornenia (ALSA) s úrovňou závažnosti Kritická, Dôležitá, Stredná alebo Nízka, pričom obsahuje strojovo čitateľné údaje OVAL a OSV a oznámenie v bezpečnostnom mailing liste.
Patching ahead of upstream
Sometimes an issue matters enough to the community that we apply a patch ahead of upstream. These are reviewed and approved by ALESCo, the AlmaLinux Engineering Steering Committee, which guides the technical direction of the distribution. When upstream ships its own fix, we re-align with it. Whenever possible or appropriate, we also send patches that we've released upstream: everyone should benefit from the work of open source. Anyone can request that a patch be considered by raising it in the ALESCo channel on chat.almalinux.org. A few examples of patches we have shipped or provided for testing:
Direct reports
How we handle an issue reported directly to us depends on what it affects. We aim to acknowledge reports within 2 to 3 days.
- OS issues that need coordinated disclosure: email security@almalinux.org so we can coordinate a responsible patch and release.
- OS issues that do not need coordination: file them at bugs.almalinux.org.
- Anything that is not the operating system itself, such as ELevate or this website: open an issue on that project's repository.
If a direct report is really an upstream issue, we point you to report it upstream so it is fixed at the source for everyone. Critical issues reported to the linux-distros mailing list are patched on the date of disclosure. See our vulnerability disclosure policy for full details.
Independent certifications
Formal, third-party certification backs our security work with independent validation. AlmaLinux OS is FIPS 140-3 validated and Common Criteria certified, with more underway.
GPG keys
AlmaLinux signs all packages with a GPG key, verified by default by dnf and graphical update tools. We recommend verifying a package signature before installing.
AlmaLinux OS 10 / AlmaLinux OS Kitten 10
EE6D B7B9 8F5B F5ED D9DA 0DE5 DEE5 C11C C2A1 E572
AlmaLinux OS 9
BF18 AC28 7617 8908 D6E7 1267 D36C B86C B86B 3716
AlmaLinux OS 8 #2
BC5E DDCA DF50 2C07 7F15 8288 2AE8 1E8A CED7 258B
ELevate
74E7 F249 EE69 8A4D ACFB 48C8 4297 85E1 81B9 61A5
Expired but remains a trusted key.
AlmaLinux OS 8 #1
5E9B 8F56 17B5 066C E920 57C3 488F CF7C 3ABB 34F8
Secure Boot certificates
AlmaLinux provides Secure Boot support starting with the 8.4 release. Its shim passes the official review and is signed by Microsoft. The AlmaLinux shim trusts these certificates:
Current
| Certificate | Signed for: | Verified by: | Validity |
|---|---|---|---|
| almalinux-sb-cert-3.der | AlmaLinux Secure Boot CA | AlmaLinux Secure Boot CA | Expires 14.03.2034 |
Predchádzajúca
These certificates have expired but remain trusted.
| Certificate | Signed for: | Verified by: | Validity |
|---|---|---|---|
| almalinux-sb-cert-1.der | AlmaLinux OS Foundation | Sectigo Public Code Signing CA EV R36 | Expired 30.01.2025 |
| almalinux-sb-cert-2.der | AlmaLinux OS Foundation | SSL.com EV Code Signing Intermediate CA RSA | Expired 19.01.2025 |
Stay in the loop
Report a vulnerability, subscribe for advisories, or talk security with us directly.
